Related Topics:
Battery Storage Remote Access-
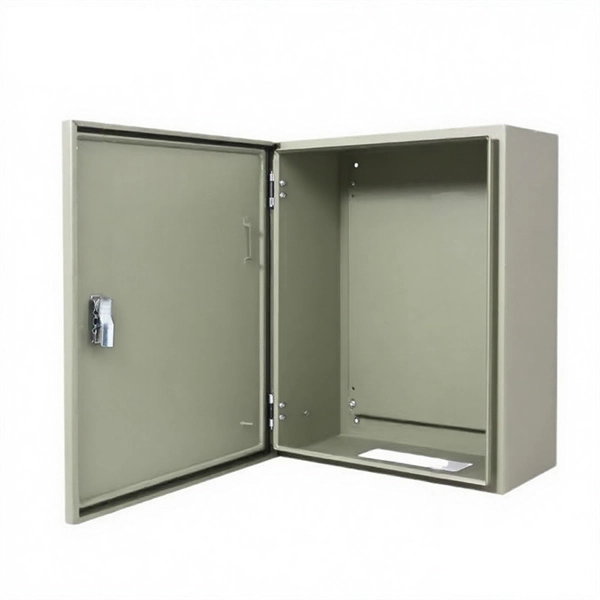
What materials are used in lithium battery energy storage cabinets
Energy storage cabinets primarily utilize 1. advanced composite materials, 2. These materials can endure various temperatures and environmental conditions, making them. Selecting the right battery enclosure material is a key step in lithium battery system design. The enclosure is not just a protective shell. It affects thermal management, safety, durability, and long-term reliability. For most lithium battery systems, engineers choose between two main options:. A lithium battery cabinet is typically constructed from double-walled, cold-rolled steel with a fire-resistant insulation core made of materials like calcium sulphate and high-density fibre panels. These layers act as thermal barriers, withstanding external fires for up to 90–120 minutes, giving. Lithium battery energy storage cabinets are revolutionizing industries from renewable energy to commercial power management. This article breaks down their manufacturing process, highlights industry applications, and shares data-driven insights to help businesses understand their value. Ventilation System: Built-in ventilation minimizes heat accumulation and prevents hazardous.
[PDF Version]
-
Access Control for Network Security Devices
NAC, meaning Network Access Control, is an advanced cybersecurity measure regulating which entities gain access to which specific network resources. Beyond traditional security parameters, NAC enforces specific access policies, ensuring only compliant devices and authorized users. Network access control, or NAC, solutions support network visibility and access management through policy enforcement on devices and users of corporate networks. Identifies devices attempting to connect. Policies may be based on authentication, endpoint configuration. Upgrading from password- to certificate-based authentication with a Public Key Infrastructure (PKI) significantly strengthens NAC frameworks.
[PDF Version]
FAQs about Access Control for Network Security Devices
What is network access control (NAC)?
Network access control (NAC) is the process of restricting unauthorized users and devices from gaining access to a corporate or private network.
What are the advantages of network access control?
Network access control comes with a number of benefits for organizations:Control the users entering the corporate networkControl access to the appl...
What is the importance of network access control?
Network access control helps in many areas, but specifically provides: Improved Security, Saves Costs, Automation, Enhanced IT Experiences, and Eas...
-
Inter-switch access links
The ISL is proprietary of Cisco and is used only between Cisco switches. It operates in a point-to-point VLAN environment and supports up to 1000 VLANs and can be used over Fast Ethernet and Gigabit Ethernet links only. When a switch port works in access mode, it is called an access port. Configuration of VLANs other than VLAN 1 then to carry traffic of these VLANs, user has to make a switch port trunk which is connected to another switch. Cisco recommends that you have knowledge of VLANs and trunking. ISL works by encapsulating a frame in an ISL.
[PDF Version]
-
Eor access switch
An EoR (End-of-Row) switch is a network switch placed at the end of a data-center rack row, aggregating connections from multiple server racks into a centralized switching point. All servers in the row connect to the EoR switch using structured horizontal cabling, typically copper. In contrast to the TOR architecture, EOR architecture provides unified network access points at the end of each row of cabinets. Datacenter architecture design is largely dependent on data communication and the interconnection of switches. When there are a lot of servers to connect (like in a Data Center), networking needs to be flexible/scalable enough to handle the computing power required for large installations.
[PDF Version]
-
Passive Fiber Optic User Access Equipment and Routers
A passive optical network (PON) is a fiber-optic telecommunications network that uses only unpowered devices to carry signals, as opposed to electronic equipment. In practice, PONs are typically used for the last mile between Internet service providers (ISP) and their customers. In this use, a PON has a point-to-multipoint topology in which an ISP uses a single device to serve many end-us. Components and characteristicsA passive optical network consists of an (OLT) at the service provider's central office (hub), passive (non-power-consuming) optical splitters, and a number of (ONUs) or Passive optical networks were first proposed by in 1987. Two major standard groups, the (IEEE) and the. A PON takes advantage of (WDM), using one wavelength for downstream traffic and another for upstream traffic on a (ITU-T, typically OS2). BPON, EP.
[PDF Version]
-
Aggregation Layer Switches and Access Layer
The aggregation or distribution switches are the intermediary layer between the core and access layers. The lowest tier is the access layer, which is used to connect all of the various end devices, such as PCs, printers, and other network components such as routers or access. The three layers of a traditional three-layer network design are the core layer, aggregation layer, and access layer. Together, these layers can offer consumers a network that is safe, reliable, and affordable. The following major topics are included: • Data. Data Center Basic Layered Design of Core, Aggregation, and Access The data center network design is based on a proven layered approach, which has been tested and improved over the past several years in some of the largest data center implementations in the world. The layered approach is the basic. If a campus network is part of an enterprise network, it allows end users and devices to access network services and resources within the same geographic area or in proximity. It facilitates the connectivity because it would rapidly become impractical to.
[PDF Version]
-
The connected switch has no network access
To fix network connection issues on a switch, start by checking physical connections and cables. Reboot the switch and connected devices. Check for firmware updates and apply if necessary. Check LED lights. on switch I also have the dhcp server setup with a different VLAN ID (rebooted all the devices modem, router and switch) connected the workstation. Whether using a managed or unmanaged switch, diagnosing and fixing switch failures requires a structured approach.
[PDF Version]
-
China Unicom Broadband Access Layer 2 Switch
With the steady development of 5G networks and applications, 5G services are becoming increasingly differentiated, convergent, and diversified. However, uplink bandwidth remains a bottleneck. Mobile br.
[PDF Version]